Repository navigation
feat: agent vault mcp server - #8672
Conversation


|
💬 Discussion in Slack: #pr-review-infisical-8672-feat-mcp-proxy Posted by Review Police — reviews, comments, new commits, and CI failures will stream into this channel. |

Codex Review SummaryThis comment shows the latest Codex review activity on this pull request.
ℹ️ About Codex in GitHubYour team has set up Codex to review pull requests in this repo. Reviews are triggered when you
Codex reacts with 👀 while any review is running, comments if it has suggestions, and reacts with 👍 once all reviews finish with no findings. |
|
Codex usage limits have been reached for code reviews. Please check with the admins of this repo to increase the limits by adding credits. |

|
Review the following changes in direct dependencies. Learn more about Socket for GitHub.
|


 [High impact] The PR appears safe to merge, with two non-blocking improvements to refresh frequency and outage feedback. Findings
|



 sheensantoscapadngan
changed the title
sheensantoscapadngan
changed the title

|
Preview deployment for your docs. Learn more about Mintlify Previews.
💡 Tip: Enable Automations to automatically generate PRs for you. |


- Drop the box, shield icon and badges; one status line, one sentence and one button per state
- Before authorizing, show only "Authorize with <host>"; waiting lives in the button with Cancel
- Use the shared status labels, a fixed "Authorized on" date, and plain-text scopes that wrap and collapse after 10
- Show a failed refresh as one line with the server's reason on hover, muted under Needs Additional Scopes
- Keep the saved scopes visible when a reauthorization fails
- "Use your own OAuth app" link on first connect too, with the redirect URI, an instruction and side-by-side client fields
- Auth Method as a Select, "Advanced Options" label, and the Sends preview only when a header is customized
- Rename "OAuth 2.1" to "OAuth", drop the unused popup-closed tracking, and keep the callback popup open on failure
- Update mcp-servers.mdx for the new labels

…feat-agent-vault-mcp-proxy

# Conflicts:
#	backend/package-lock.json
#	backend/package.json
#	backend/src/@types/fastify.d.ts
#	backend/src/ee/routes/v1/agent-vault-routers/agent-vault-access-bundle-router.ts
#	backend/src/ee/services/agent-vault-access-bundle/agent-vault-access-bundle-service.ts
#	backend/src/ee/services/agent-vault-proxy/agent-vault-proxy-service.ts
#	backend/src/server/routes/index.ts
#	frontend/src/components/agent-vault/ServiceIconStack.tsx
#	frontend/src/components/agent-vault/service-sheet/ServiceSheet.tsx
#	frontend/src/components/agent-vault/service-sheet/serviceSchema.ts
#	frontend/src/components/agent-vault/service-sheet/stepMeta.ts
#	frontend/src/pages/agent-vault/AgentVaultAccessBundleDetailPage/AgentVaultAccessBundleDetailPage.tsx

…eensantoscapadngan/feat-agent-vault-mcp-proxy

# Conflicts:
#	backend/e2e-test/routes/v1/agent-vault.spec.ts
#	backend/src/@types/fastify.d.ts
#	backend/src/db/sanitized-schema.yaml
#	backend/src/db/schemas/agent-vault-services.ts
#	backend/src/ee/routes/v1/agent-vault-routers/agent-vault-access-bundle-router.ts
#	backend/src/ee/routes/v1/agent-vault-routers/agent-vault-proxy-agent-router.ts
#	backend/src/ee/routes/v1/agent-vault-routers/agent-vault-schemas.ts
#	backend/src/ee/services/agent-vault-access-bundle/agent-vault-access-bundle-service.ts
#	backend/src/ee/services/agent-vault-access-bundle/agent-vault-access-bundle-types.ts
#	backend/src/ee/services/agent-vault-access-bundle/agent-vault-service-dal.ts
#	backend/src/ee/services/agent-vault-proxy/agent-vault-proxy-service.ts
#	backend/src/ee/services/agent-vault/AGENTS.md
#	backend/src/keystore/keystore.ts
#	backend/src/server/routes/index.ts
#	docs/documentation/platform/agent-vault/plan-your-setup.mdx
#	docs/documentation/platform/agent-vault/proxies.mdx
#	docs/documentation/platform/agent-vault/services.mdx
#	docs/documentation/platform/agent-vault/session-logs.mdx
#	frontend/src/components/agent-vault/ServiceTemplateSelect.tsx
#	frontend/src/components/agent-vault/service-sheet/CredentialFields.tsx
#	frontend/src/components/agent-vault/service-sheet/ReviewFields.tsx
#	frontend/src/components/agent-vault/service-sheet/ServiceSheet.tsx
#	frontend/src/components/agent-vault/service-sheet/serviceSchema.ts
#	frontend/src/components/agent-vault/service-sheet/stepMeta.ts
#	frontend/src/hooks/api/agentVault/mutations.tsx
#	frontend/src/hooks/api/agentVault/queries.tsx
#	frontend/src/hooks/api/agentVault/types.ts
#	frontend/src/pages/agent-vault/AgentVaultAccessBundleDetailPage/components/ServicesCard.tsx

|
| GitGuardian id | GitGuardian status | Secret | Commit | Filename | |
|---|---|---|---|---|---|
| 38833010 | Triggered | Username Password | 7fa9d1e | backend/src/ee/services/agent-vault-access-bundle/agent-vault-credential-write-fns.test.ts | View secret |
| 38833011 | Triggered | Generic Password | 7fa9d1e | backend/src/ee/services/agent-vault-access-bundle/agent-vault-credential-write-fns.test.ts | View secret |
| 38911126 | Triggered | Username Password | 7fa9d1e | backend/e2e-test/routes/v1/agent-vault.spec.ts | View secret |
🛠 Guidelines to remediate hardcoded secrets
- Understand the implications of revoking this secret by investigating where it is used in your code.
- Replace and store your secrets safely. Learn here the best practices.
- Revoke and rotate these secrets.
- If possible, rewrite git history. Rewriting git history is not a trivial act. You might completely break other contributing developers' workflow and you risk accidentally deleting legitimate data.
To avoid such incidents in the future consider
- following these best practices for managing and storing secrets including API keys and other credentials
- install secret detection on pre-commit to catch secret before it leaves your machine and ease remediation.
🦉 GitGuardian detects secrets in your source code to help developers and security teams secure the modern development process. You are seeing this because you or someone else with access to this repository has authorized GitGuardian to scan your pull request.
…feat-agent-vault-mcp-proxy


Context
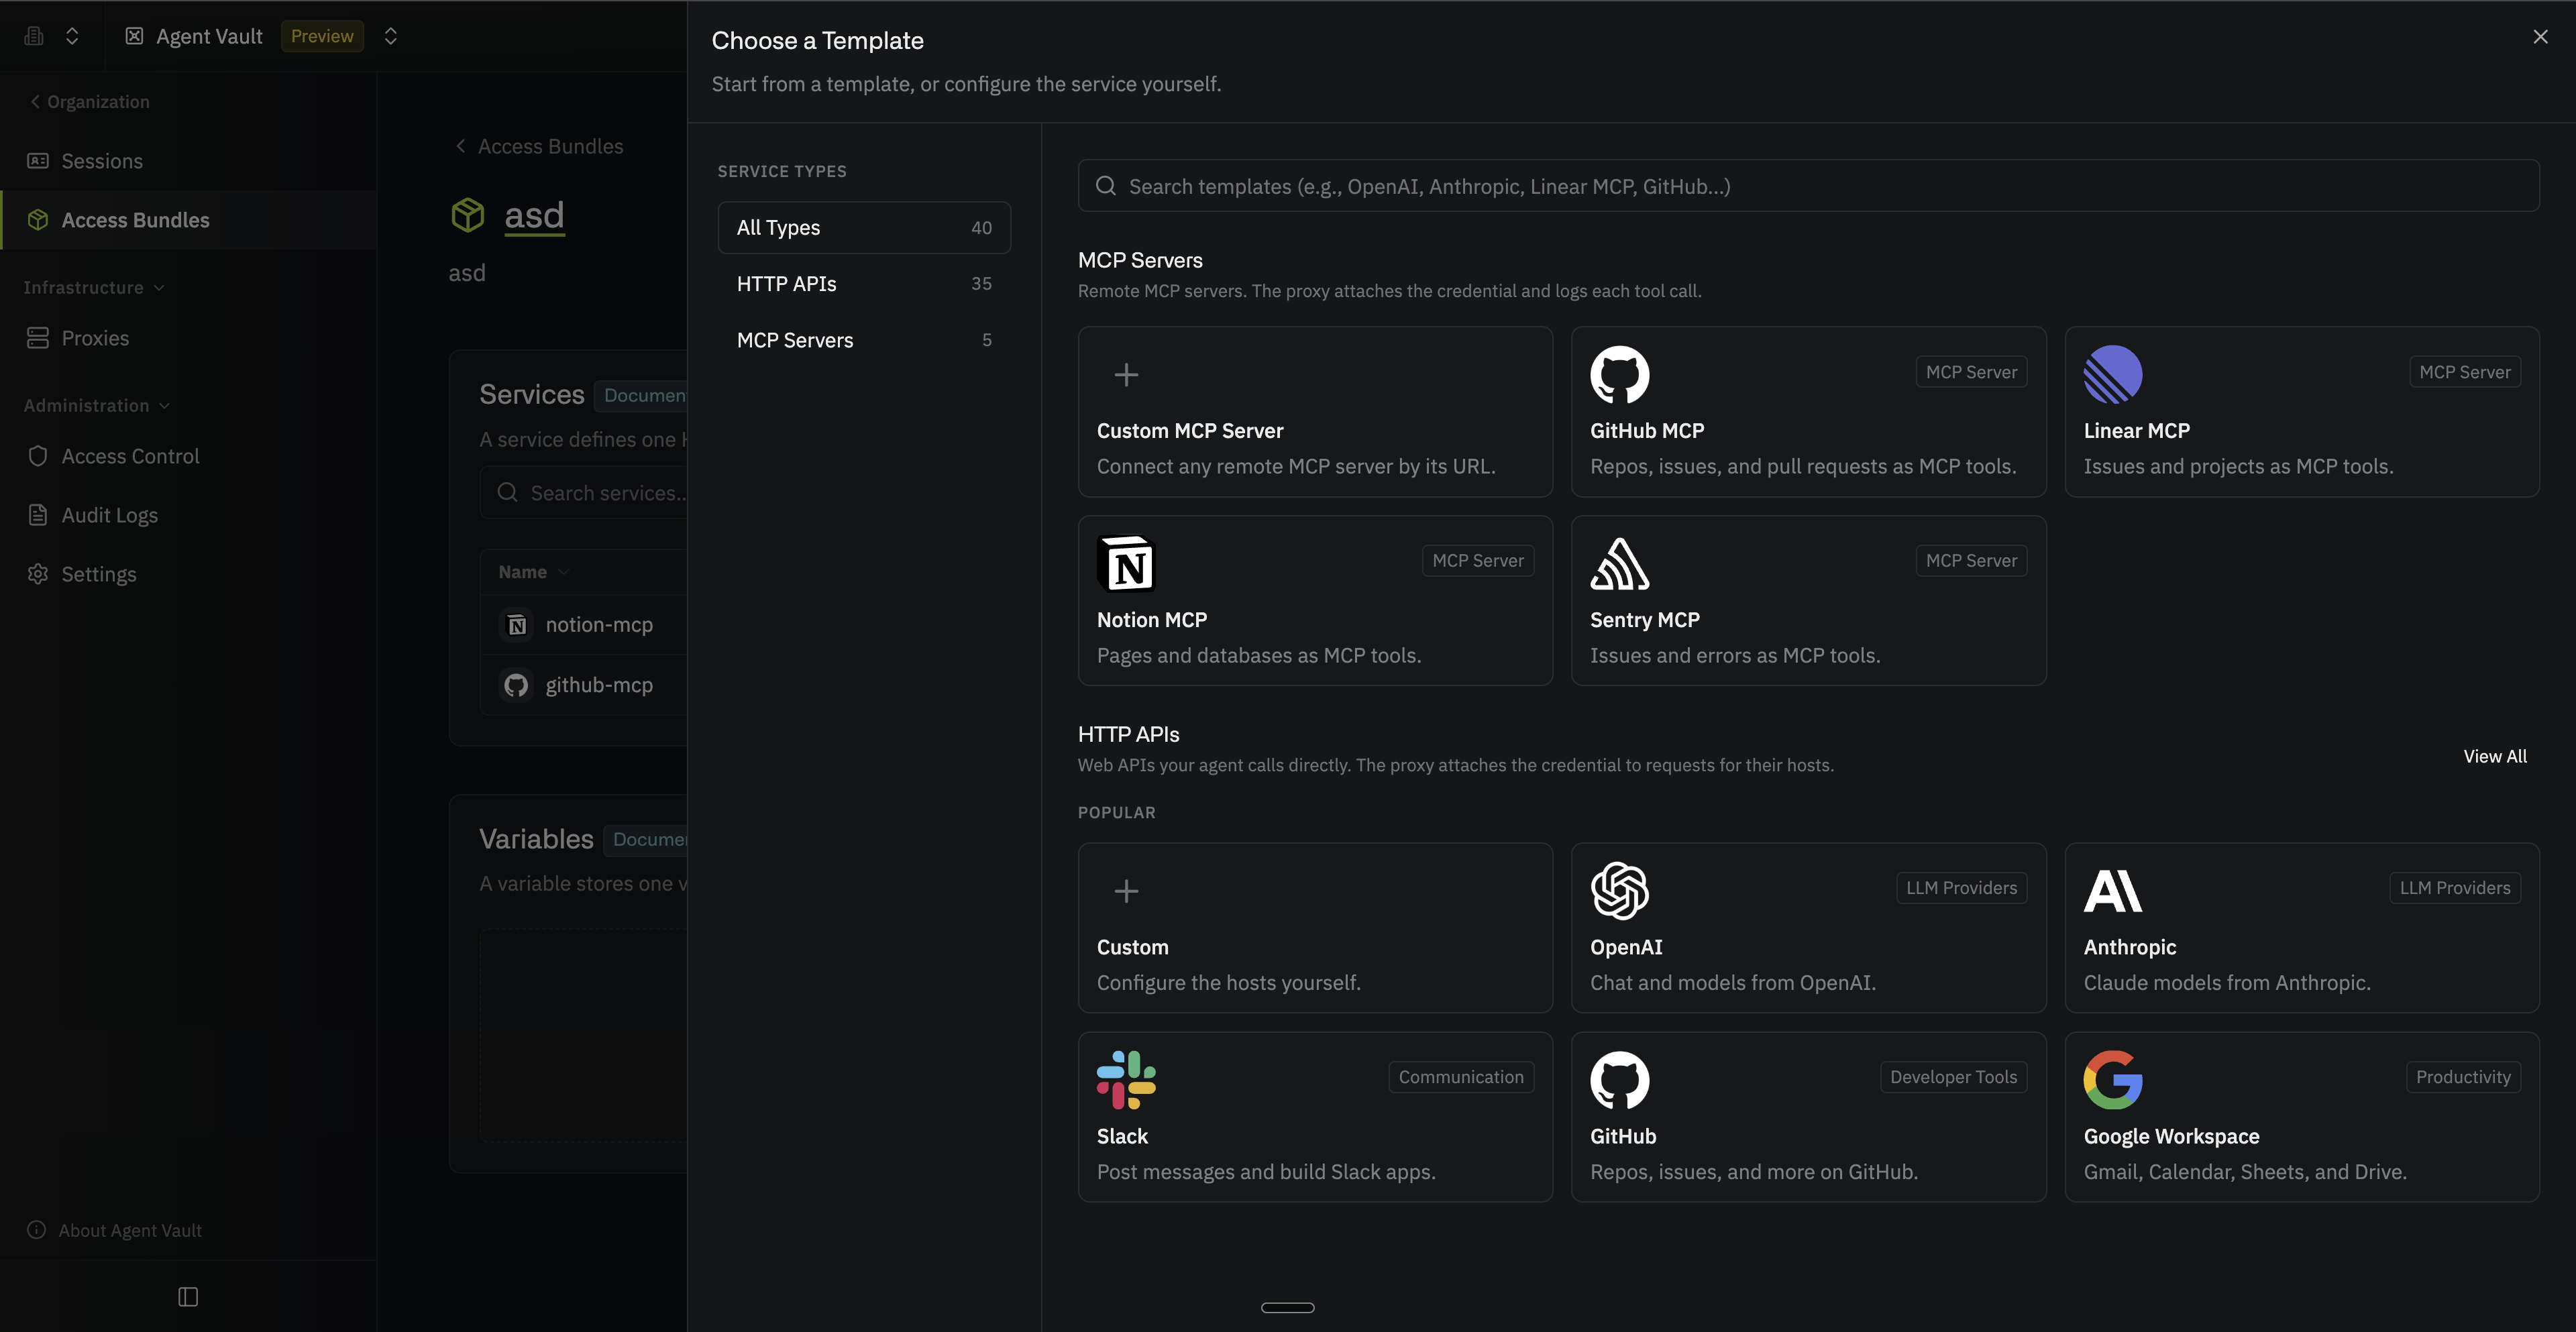
This PR adds support for MCP proxying via Agent Vault
Relevant PR:
Infisical/cli#436
Screenshots
Steps to verify the change
Type
Checklist
type(scope): short description(scope is optional, e.g.,fix: prevent crash on syncorfix(api): handle null response).